CMMC LEVEL 2 · NIST SP 800-171 REV 2 → REV 3

Don't just pass CMMC. Don't make a false claim.

Your CMMC Level 2 attestation is a legal promise to the U.S. Government. One inaccurate SPRS score can cost you your contract — and trigger a False Claims Act lawsuit. We make you Self-Attestation Ready, DIBCAC Ready, and FCA-proof.

SELF-ATTESTATION READY · DIBCAC READY · FCA-PROOF

WHAT YOU ATTEST TO DFARS 252.204-7021
110 Rev 2 requirements in today's affirmation
320 Assessment objectives DIBCAC tests
422 Rev 3 objectives across 97 requirements
88 Rev 3 parameters you must define yourself
IF THE CLAIM IS FALSE Treble damages + $14,308 – $28,619 per claim, plus suspension, debarment and loss of DoD contracts.
THE RISK

Self-attestation is not self-declaration. It's a legal claim.

Under CMMC 2.0, a senior official affirms that your organization meets all 110 requirements of NIST SP 800-171 Rev 2. That affirmation is legally binding — and DIBCAC or another external auditor can validate it at any time.

01

You attest, you risk.

Every CMMC Level 2 affirmation is signed by a senior official. If your evidence doesn't match your claim, DOJ can pursue you under the False Claims Act — treble damages plus up to $28,619 per claim. We make sure you never attest to what you can't prove.

02

Rev 2 today, Rev 3 tomorrow.

CMMC is on NIST 800-171 Rev 2 today — 110 controls. Rev 3 is coming — 97 controls, 422 objectives, 88 numbers you must define. We build you to pass Rev 2 now and transition to Rev 3 without redoing the work.

03

Your subcontractor is your risk.

Rev 3 adds Supply Chain Risk Management as a full control family. If you pass up a subcontractor's claim you didn't verify, that false claim becomes yours. We validate the whole chain.

How good contractors accidentally create false claims

Most False Claims Act cases in cybersecurity don't start with fraud. They start with a mistake:

1 You submit an SPRS score of 110 based on planned controls, not implemented controls.
2 You attest to NIST 800-171 compliance while POA&M items are still open and not disclosed.
3 You copy a generic SSP that describes controls you don't actually have.
4 You certify DFARS 252.204-7021 compliance without logs, screenshots, or evidence.
5 A subcontractor tells you they're compliant — you pass that claim up to the Prime, and the Prime passes it to DoD.
31 U.S.C. § 3729 · FALSE CLAIMS ACT

The government doesn't need to prove you intended to lie. Reckless disregard or deliberate ignorance is enough.

You don't need to have been breached to face liability. You just need to have claimed compliance you couldn't prove. DOJ's Civil Cyber-Fraud Initiative has already settled multi-million dollar cases for this exact pattern.

Penalties (2025 adjusted) Treble damages + $14,308 to $28,619 per false claim, plus suspension, debarment, and termination of DoD contracts.
Avoid the claim. Don't defend it later. We don't help you explain an inaccurate attestation after the fact. We prevent you from making it.
OUR AVOIDANCE FRAMEWORK

Four pillars. No claim you can't prove.

A program built so you never create a false claim in the first place — not protection after the fact.

PILLAR 01

Truthful scoping

We define exactly what CUI you handle, where it lives, and what is in scope. Too broad inflates your SPRS score; too narrow hides gaps. We document the true boundary — in writing — before any score is submitted.

PILLAR 02

Evidence before attestation

No control is marked "Implemented" without evidence. If it isn't documented, it isn't done. Each of the 110 Rev 2 requirements gets a linked artifact — screenshot, log, policy, configuration, or interview record.

PILLAR 03

Honest POA&M & SPRS scoring

We calculate your true SPRS score using the DoD methodology and keep your POA&M open, dated, and current. If your score is inflated, we help you correct it proactively — with a timeline that shows good faith, not concealment.

PILLAR 04

Flow-down control

We validate your subcontractors before you attest on their behalf. No flow-down claim without flow-down evidence — and a vendor attestation pack that makes your prime claim defensible.

WHAT CHANGED

NIST 800-171 Rev 2 to Rev 3, at a glance.

Build only for Rev 2 and you rebuild your documentation later. Jump to Rev 3 too early and you fail a current Rev 2 audit. You need a dual-track strategy.

REV 2 · CURRENT BASELINE REV 3 · FUTURE BASELINE
PublishedFebruary 2020May 14, 2024
Requirements11097
Control families1417 — adds Planning (PL), System & Services Acquisition (SA), Supply Chain Risk Management (SR)
Assessment objectives320422
Organization-Defined ParametersNone88 — you define values like logon attempts, timeframes, and review cycles
Key change"Periodically" language allowed"Periodically" removed — specific timeframes required

Why Rev 3 raises your FCA risk

Fewer controls, more scrutiny. 110 controls consolidate to 97, but objectives jump from 320 to 422. Each one is a claim you must prove.
ODPs are your own numbers. You define your patch window, logon lockout, and account review cycle. Auditors test against your numbers — if you define them but don't meet them, your own policy proves the claim false.
Supply chain is now in scope. Attesting to supply chain risk management without validating subcontractors is direct FCA exposure flowing down to you.
Your SSP must be rebuilt. Structure, numbering, and mapping to NIST 800-53 Rev 5 all change. A copy-paste Rev 2 SSP won't pass a Rev 3 audit — and a generic SSP is exactly what DOJ points to in FCA cases.
CRITICAL FACT

CMMC Level 2 self-assessments and DIBCAC assessments are still conducted against Rev 2 under DoD Class Deviation 2024-O0013. Rev 3 is not yet required — but DoD published its Rev 3 ODPs in April 2025.

The transition is coming, and organizations that wait will be caught in the audit backlog. We build you for Rev 2 today with Rev 3 architecture — so you avoid a second, rushed transition that creates inaccurate attestations.

Get your Rev 2 to Rev 3 gap analysis
SERVICES · BUILT TO AVOID FCA

Self-attestation ready. DIBCAC ready. FCA-defensible.

End to end — from your first true score to the day your senior official signs, and every annual affirmation after.

01 · REV 2 BASELINE

FCA Avoidance Gap Assessment

We assess all 110 Rev 2 controls and review your current SPRS score, prior attestations, and DFARS representations for FCA exposure. You get a Truthful Score vs. Submitted Score report, with a correction plan.

02 · TRANSITION

Rev 2 to Rev 3 Transition Plan

Control-by-control mapping: what carries over, what was withdrawn or consolidated, what is new (PL, SA, SR), and which ODPs you must define — before you ever claim Rev 3 readiness.

03 · DOCUMENTATION

Audit-Ready SSP, POA&M & Evidence Library

SSP, network diagram, CUI data flow, asset inventory, and every policy — written for your environment, not from a template. Every statement is tied to a verifiable artifact. No evidence, no claim.

04 · IMPLEMENTATION

Remediation & Implementation Support

We fix gaps with you: MFA and access control, logging and SIEM, vulnerability management, encryption, media protection, secure configuration, and supply chain controls — with weekly evidence check-ins.

05 · READINESS

DIBCAC Readiness & Mock Audit

A mock assessment using the same 320 Rev 2 determination statements DIBCAC will use (and 422 for Rev 3 planning), plus interview prep and evidence validation — so your senior official signs with confidence.

06 · ONGOING

SPRS Integrity Program

Annual affirmation support, POA&M maintenance, continuous monitoring, and SPRS score updates. Your score stays accurate year-round — no drift, no stale claims.

OUR 4-STEP FAST TRACK

From gap to attestation-ready in 3–6 months.

Timelines depend on your starting maturity. DIBCAC audit windows are limited — starting now protects your contracts and your legal position.

  1. STEP 1 30 MIN · FREE

    FCA avoidance call

    We review your current SPRS score, contract flow-downs, CUI scope, and timeline — and flag any immediate FCA risk. No obligation.

  2. STEP 2 2–3 WEEKS

    Gap assessment + FCA review

    Your true score vs. your submitted score, a Rev 2 to Rev 3 map, and a correction plan with costs and timeline.

  3. STEP 3 8–16 WEEKS

    Build & remediate

    We build your SSP and evidence library and remediate gaps with weekly checkpoints. Every closure is documented.

  4. STEP 4 READY

    Attest with confidence

    We validate all evidence, finalize your SPRS score and POA&M, and prepare your senior official to affirm. You attest to what you can prove — nothing more, nothing less.

PACKAGES & PRICING

CMMC compliance services for defense contractors.

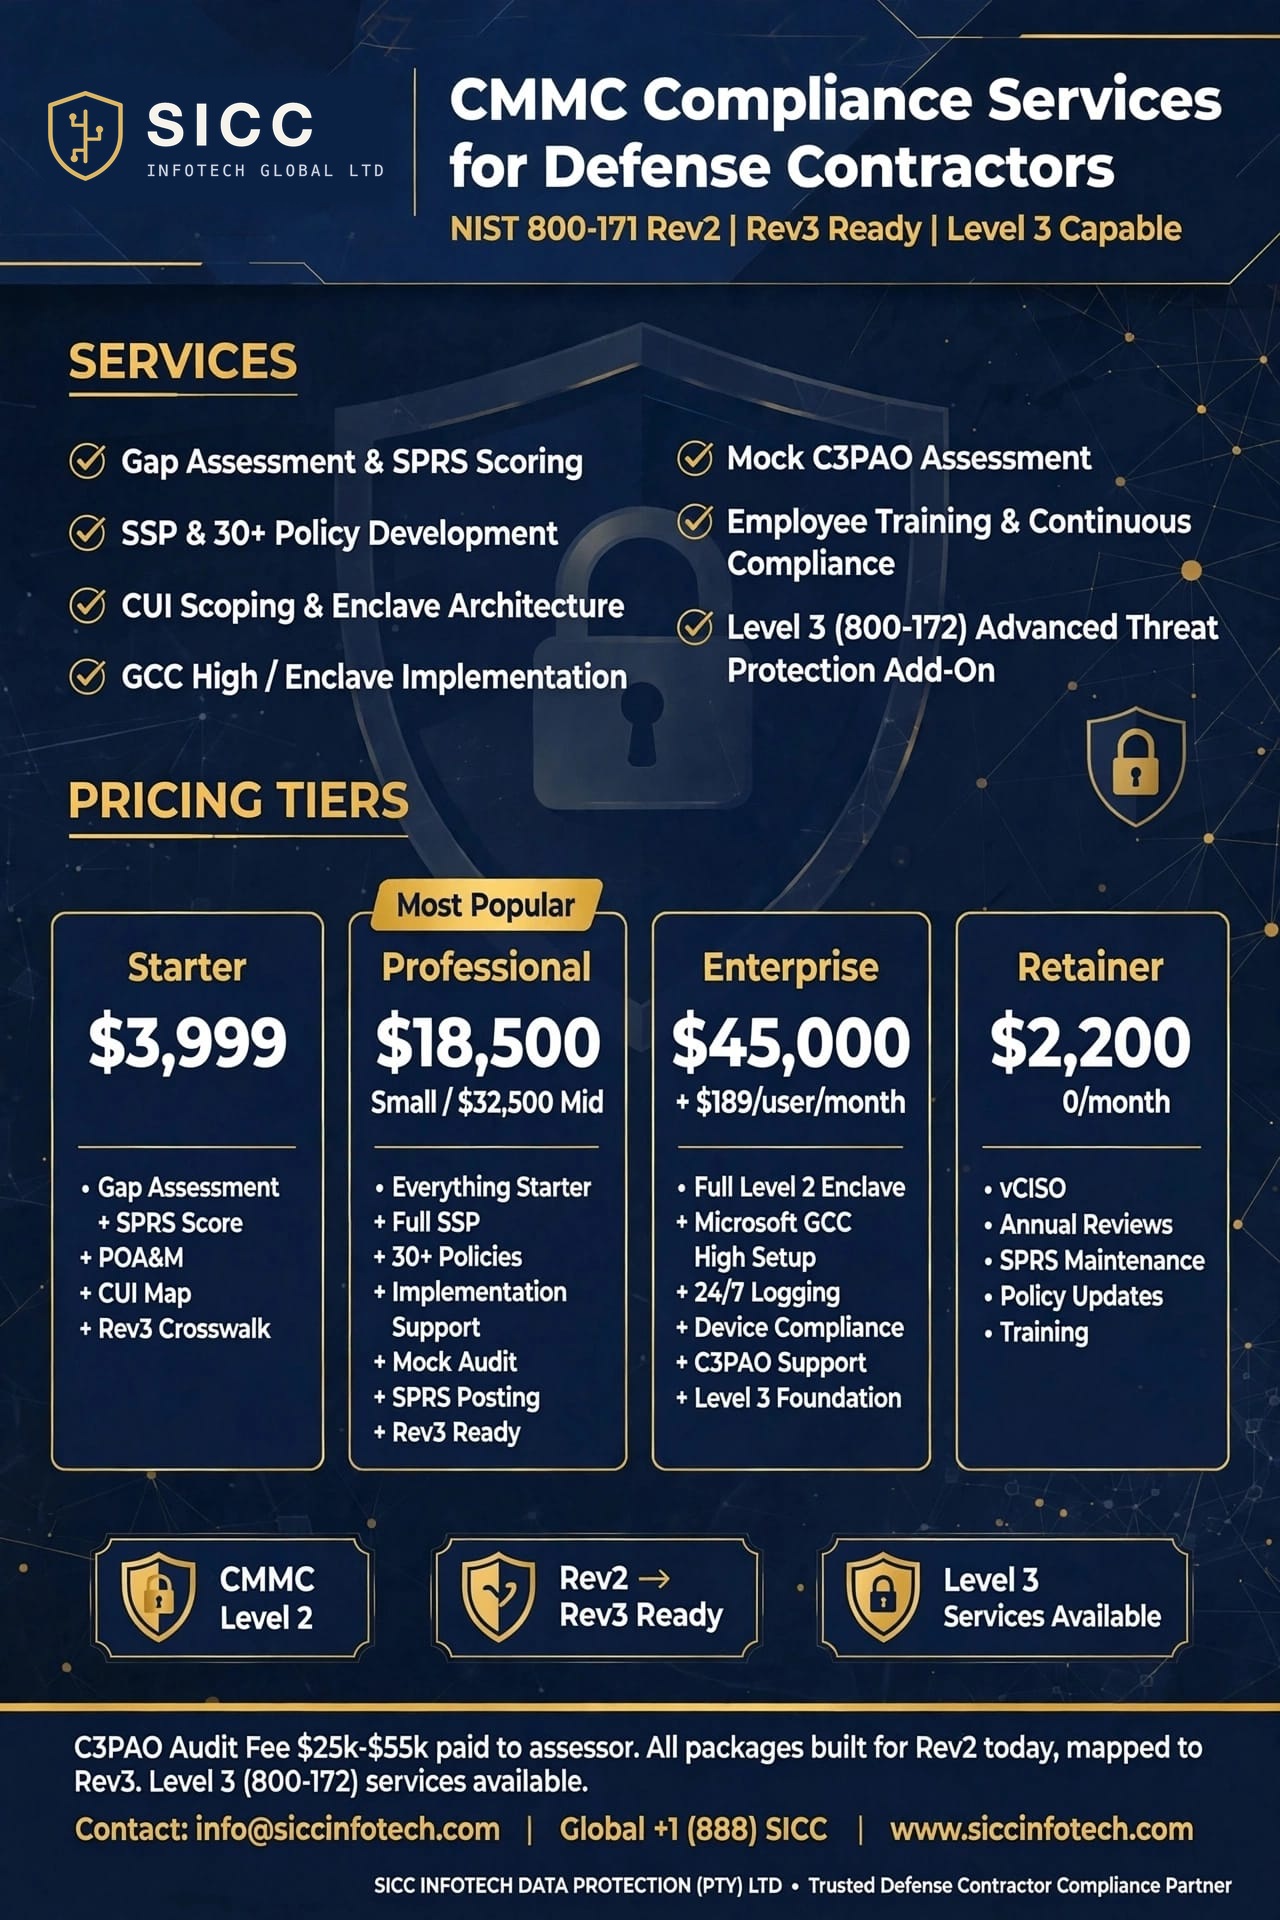
SICC Infotech CMMC compliance services flyer: services list and pricing tiers (Starter, Professional, Enterprise, Retainer) DOWNLOAD THE FLYER
WHAT YOU GET · AUDIT-READY DELIVERABLES

We don't give you a template. We give you proof.

Not just a report — a complete, audit-ready package that proves your attestation is true. Ready for DIBCAC, a prime, or any external audit.

01 · ASSESSMENT & STRATEGY
CMMC Level 2 Gap Assessment ReportAll 110 controls scored against the 320 objectives, with a true vs. submitted SPRS score.
Rev 2 to Rev 3 Transition MapControl-by-control mapping to the 97 Rev 3 controls, including the PL, SA and SR families.
FCA Exposure Review & Correction PlanYour current score and prior attestations, with a documented plan to correct any inaccurate claim before audit.
CUI Scoping & Boundary MemoWhat CUI you handle, where it lives, and which systems are in or out of scope.
Remediation Roadmap & POA&MA prioritized plan with owners, dates, and the evidence required for closure.
02 · CORE DOCUMENTATION
System Security Plan (SSP)Written for your environment — not a generic template — with every control tied to evidence.
Network & CUI Data Flow DiagramsVisual proof of your enclave, boundaries, and how CUI moves through your organization.
Asset InventoryIn-scope hardware, software, cloud services, and users.
Policies & Procedures LibraryEverything required for Rev 2 and Rev 3 readiness, including: ACCESS CONTROL INCIDENT RESPONSE RISK ASSESSMENT SYSTEM & COMMS PROTECTION SUPPLY CHAIN RISK MEDIA PROTECTION CONFIGURATION MGMT
03 · EVIDENCE & PROOF
Evidence LibraryScreenshots, logs, configurations, and records for every control — organized by control number for DIBCAC or external auditor review.
SPRS Score Justification PackageA defensible calculation of your true score, with evidence for every point claimed.
ODP Definitions Document (Rev 3 ready)All 88 Organization-Defined Parameters — logon attempts, patch windows, account review cycles — so your policies match your actual practice.
04 · READINESS & ATTESTATION
Mock DIBCAC Audit ReportUsing the same 320 Rev 2 determination statements (and 422 for Rev 3), with findings and remediation closure.
Interview Prep PackThe questions auditors ask, sample answers, and role assignments for your team.
Senior Official Attestation PackPrep pack and legal review checklist so your senior official signs the affirmation with confidence.
Continuous Monitoring PlanPOA&M updates, annual affirmation, and evidence refresh after certification.
NO GENERIC TEMPLATES · NO INFLATED SCORES · NO FALSE CLAIMS

WHO WE HELP

Primes, subcontractors & suppliers in the Defense Industrial Base.

Organizations that handle CUI and need to be ready for DIBCAC, a customer audit, or a prime flow-down — and want to stay out of DOJ's crosshairs. This is for you if you are:

  • Handling CUI under DFARS 252.204-7021
  • Preparing a CMMC Level 2 self-attestation and affirmation
  • Subject to (or expecting) a DIBCAC High or Medium Assessment, or any customer, prime, or DoD audit
  • Already Rev 2 compliant and need to move to Rev 3 — or starting from zero
  • Concerned about FCA exposure from an inaccurate SPRS score or attestation
Industries we serve
AEROSPACE & DEFENSE MANUFACTURING IT & MSPs SERVING DoD ENGINEERING SERVICES LOGISTICS & SUPPLY CHAIN RESEARCH & DEVELOPMENT
FAQ

Straight answers.

Do I need Rev 2 or Rev 3 for self-attestation right now?

Rev 2. Self-attestation and DIBCAC assessments are still on NIST 800-171 Rev 2 under DoD Class Deviation 2024-O0013. We build you to be Rev 3 ready now, so you don't have to rush — and risk an inaccurate attestation — later.

What is the difference between self-attestation and a DIBCAC assessment?

Self-attestation is your senior official affirming you meet all 110 Rev 2 requirements. DIBCAC is the DoD assessment team that validates that attestation through evidence review, interviews, and testing. We prepare you for both.

How does the False Claims Act apply to CMMC?

When you submit an SPRS score or CMMC attestation, you are making a representation tied to payment under your contract. If it is knowingly false — or made with reckless disregard for the truth — DOJ can pursue it under 31 U.S.C. § 3729. Contractors have paid millions in settlements for misrepresenting NIST 800-171 compliance. Our program makes sure your attestation matches your evidence.

What is the DOJ Civil Cyber-Fraud Initiative?

Launched in 2021, it uses the False Claims Act to pursue contractors who knowingly misrepresent their cybersecurity compliance. DOJ has settled cases for $4M to $11M+ over inaccurate NIST 800-171 compliance claims.

Can we correct an inaccurate SPRS score without triggering FCA liability?

Correct it proactively, document it, and remediate. DOJ looks at intent and good faith, so voluntary correction with a clear timeline is your best protection. Waiting until an audit or whistleblower finds it is the worst position to be in.

If my subcontractor is non-compliant, am I liable?

If you flow that claim up to the Prime or DoD, yes — both parties can carry FCA risk. If a subcontractor handles CUI, the requirement flows down under DFARS, and supply chain controls are a core part of Rev 3. We validate subcontractors and document flow-down compliance before you attest.

We're already Rev 2 compliant. What do we need for Rev 3?

A transition assessment. You will need to define ODPs, implement the three new families, restructure your SSP, and collect additional evidence for the 422 determination statements. We map it for you.

How long does it take to become attestation-ready?

Typically 3–6 months for remediation plus evidence validation. Organizations that start late face 9–12 month timelines because of audit scheduling and resource constraints.

What if we're not sure what CUI we handle?

That's where we start. Scoping CUI and defining your assessment boundary is step one. Too broad a scope wastes money; too narrow risks audit failure and FCA exposure.

GET READY THE RIGHT WAY

Don't risk your contracts. Don't risk a false claim.

The contractors who win aren't the ones who score 110 the fastest. They're the ones who can prove every point of that 110.

Serving the Defense Industrial Base. No jargon. No generic templates. Built to pass an audit — and built to avoid a false claim.

Book your free FCA avoidance assessment
Or request the FCA Avoidance Checklist We use your details only to respond to this request.